Cifas fraud risk data, now built into ThirdEye.
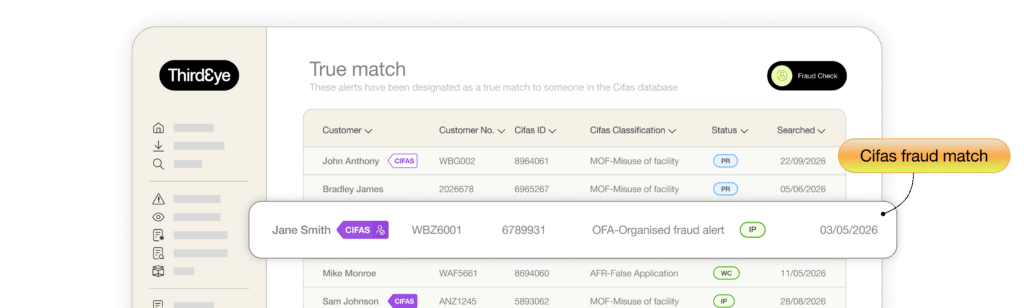
Our new Fraud Check module enables Cifas members to run Cifas NFD searches without leaving ThirdEye. Every customer search, check and note is automatically logged and linked to the customer record, creating an audit ready trail.
Trusted by
Why choose fraud check?
Search Cifas without leaving ThirdEye
Now your team can run Cifas fraud checks within their existing workflow. No separate login, no copying data between systems – just faster and more efficient checks that keeps the audit trail in one place.
Detect and act faster
Every Cifas NFD search is surfaced immediately, raising awareness of a potential fraud risk without delay. Your team spends less time hunting for information and more time making confident decisions.
Automatic audit trail
Every customer search, check and note is automatically saved and linked to the customer record. Evidence is accessible through ThirdEye’s audit reports, so the work is already done when it’s time for your annual Cifas Compliance Review.
Clear and simple search format
Cifas NFD searches are presented in a clean and consistent format alongside your teams other screening data. The team can quickly review findings, confirm true matches and move on.
FAQ
What is Cifas and why does it matter?
Cifas is the UK’s leading fraud prevention service, and its National Fraud Database (NFD) is now available within ThirdEye. The NFD holds more than 2 million fraud risk records shared by over 775 member organisations, covering identity fraud, facility takeover, false applications, false insurance claims and facility misuse. Access to this data adds a layer of protection beyond sanctions and PEP screening, so your team can spot fraud risk before it affects your business.
Do I need a separate Cifas membership to use this module?
Yes. You need a Cifas membership to access the National Fraud Database. Once your membership is in place, ThirdEye connects directly to the NFD, so your team can run searches without leaving the platform or logging into a separate system.
When can I run a Cifas check on a customer?
You can run a Cifas check on any customer at any point in their lifecycle for approved reasons: during onboarding once they’ve been added to ThirdEye, during periodic reviews, or as part of ongoing KYC. That means you’re monitoring fraud risk continuously, not just at the point of application.
How does ThirdEye record Cifas results and support my annual Compliance Review?
Every Cifas check is automatically logged, timestamped and linked to the customer record in ThirdEye. Results appear in a clear, simple format, so your team can confirm true matches quickly and move on, with no manual record-keeping or copying results between systems. Because every search and result is saved as you work, your audit trail builds itself. When your annual Cifas Compliance Review comes around, the evidence is already waiting in ThirdEye’s audit reports, with no last-minute scramble.
How does the Fraud Checks module work alongside Customer Screening?
The two modules are designed to work together. Customer Screening covers sanctions and PEPs, while Fraud Checks adds Cifas fraud risk data to the same customer profile. Your team gets a complete view of fraud and financial crime risk in one place, without switching systems or reconciling results from separate sources.